

Compliance insights
Insights from CREST-certified practitioners on the threats, regulations and technologies shaping cyber security.
Compliance
1 to 12 of 16 articles
What Is ISO 42001? The AI Management Standard Explained
ISO/IEC 42001 is the international standard for managing AI responsibly. Learn what it requires, who needs it and how it fits with ISO 27001.
Read article · 11 min
Cyber Essentials vs Cyber Essentials Plus: Which Does Your Business Need?
Cyber Essentials or Cyber Essentials Plus? Compare self-assessment and audited certification, costs, timescales and which one your contracts actually require.
Read article · 11 min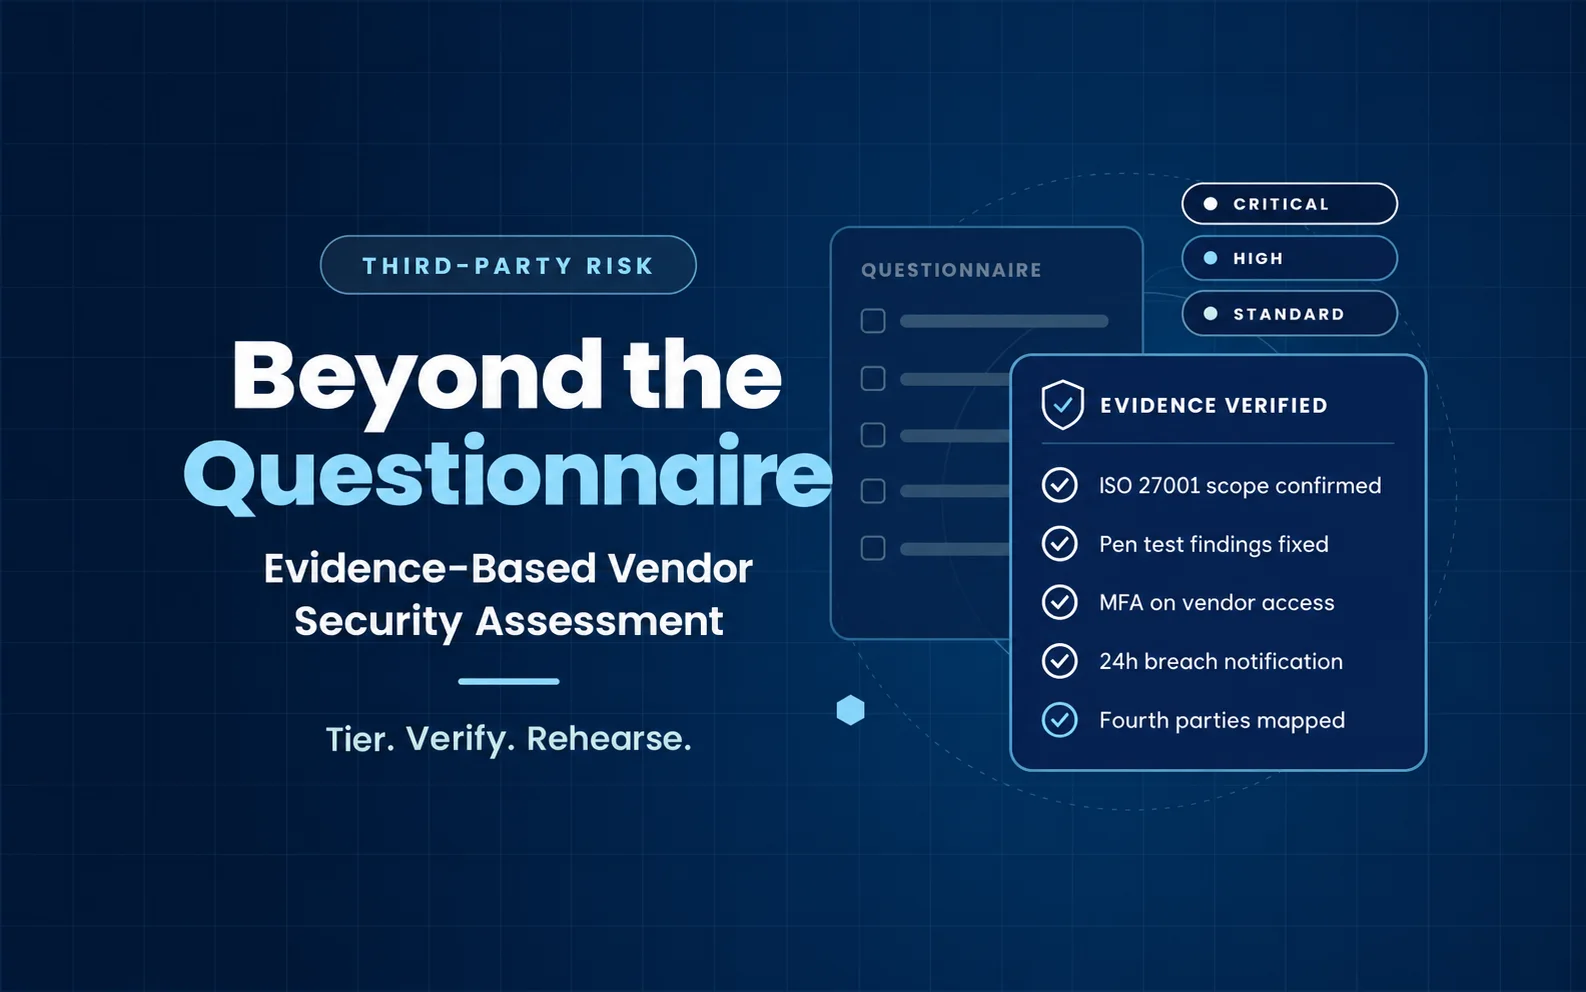
Beyond the Questionnaire: Evidence-Based Vendor Security Assessment for Security Leaders
How to assess vendor security with evidence: tier suppliers by impact, validate controls and move to continuous third-party risk management.
Read article · 10 min
Your Supplier List Is Not a Resilience Plan: A Global Guide to Third-Party Cyber Risk
Third-party cyber risk management means mapping shared dependencies, not just listing suppliers. Learn how to assess, contain and exercise supplier risk.
Read article · 14 min
Threat-Led Penetration Testing for DORA and NIS2 Compliance: What You Need to Know
Threat-led penetration testing (TLPT) is now required under DORA and supports NIS2. Learn how TLPT differs from red teaming and standard pen testing.
Read article · 11 min
DORA Compliance for Cyber Security: Your Roadmap to 2025 Readiness
DORA compliance requirements explained: who is in scope, the core obligations, how DORA compares with NIS2 and ISO 27001, and the steps to get ready.
Read article · 10 min
Legal Aid Providers: Are You Ready for December’s Cyber Essentials Deadline?
Cyber Essentials for legal aid providers becomes mandatory in December 2025. Learn the five controls, how certification works and how to meet the deadline.
Read article · 10 min
Achieving ISO 27001:2022 Compliance, Your Complete UK Consultancy Guide
How to achieve ISO 27001:2022 compliance: key requirements, common pitfalls and a readiness timeline, plus when an ISO 27001 consultant can help.
Read article · 9 min
The Ultimate Guide to Cyber Security Disaster Recovery and Business Continuity Planning
A cyber security business continuity plan keeps you running through ransomware and outages. Learn how BC/DR planning works and how to build your strategy.
Read article · 13 min
The UK Cyber Security and Resilience Bill, A New Era for Digital Infrastructure
The UK Cyber Security and Resilience Bill modernises cyber regulation for digital infrastructure. Learn who it covers, what changes and how to prepare.
Read article · 7 min
ISO/IEC 27001:2022 – October 2025 Deadline: Have You Considered the Environmental Requirement?
The ISO 27001 climate change amendment requires you to assess climate risk under clauses 4.1 and 4.2. Learn what to document before the 2025 transition audit.
Read article · 2 min
Small Business, Big Protection: How Cybergen is Helping SMEs Navigate the NIST Framework
The NIST Cybersecurity Framework for small business explained: common SME threats, the hidden cost of going cheap and practical steps to improve security.
Read article · 10 minNo articles match that search. Try a broader term.
Get expert threat intelligence in your inbox
A monthly briefing on emerging threats, regulatory changes and practical defence advice. No spam, unsubscribe anytime.